
EC-COUNCIL EC-Council Certified Security Analyst (ECSA) - ECSAv8무료 덤프문제 풀어보기
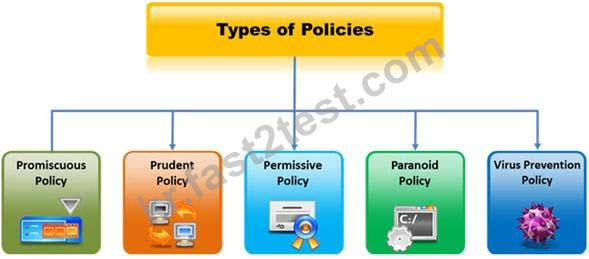
Which type of security policy applies to the below configuration? i)Provides maximum security while allowing known, but necessary, dangers ii)All services are blocked; nothing is allowed iii)Safe and necessary services are enabled individually iv)Non-essential services and procedures that cannot be made safe are NOT allowed v)Everything is logged
정답: C
Which of the following is developed to address security concerns on time and reduce the misuse or threat of attacks in an organization?
정답: B
A WHERE clause in SQL specifies that a SQL Data Manipulation Language (DML) statement should only affect rows that meet specified criteria. The criteria are expressed in the form of predicates. WHERE clauses are not mandatory clauses of SQL DML statements, but can be used to limit the number of rows affected by a SQL DML statement or returned by a query.
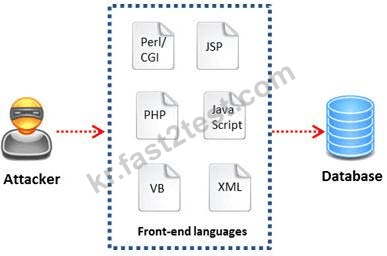
A pen tester is trying to gain access to a database by inserting exploited query statements with a WHERE clause. The pen tester wants to retrieve all the entries from the database using the WHERE clause from a particular table (e.g. StudentTable).
What query does he need to write to retrieve the information?
정답: B
Which of the following attacks does a hacker perform in order to obtain UDDI information such as businessEntity, businesService, bindingTemplate, and tModel?
정답: B
설명: (Fast2test 회원만 볼 수 있음)
James is testing the ability of his routers to withstand DoS attacks. James sends ICMP ECHO requests to the broadcast address of his network. What type of DoS attack is James testing against his network?
정답: A
Vulnerability assessment is an examination of the ability of a system or application, including current security procedures and controls, to withstand assault. It recognizes, measures, and classifies security vulnerabilities in a computer system, network, and communication channels.
A vulnerability assessment is used to identify weaknesses that could be exploited and predict the effectiveness of additional security measures in protecting information resources from attack.
Which of the following vulnerability assessment technique is used to test the web server infrastructure for any misconfiguration and outdated content?
A vulnerability assessment is used to identify weaknesses that could be exploited and predict the effectiveness of additional security measures in protecting information resources from attack.
Which of the following vulnerability assessment technique is used to test the web server infrastructure for any misconfiguration and outdated content?
정답: C
An automated electronic mail message from a mail system which indicates that the user does not exist on that server is called as?
정답: A
설명: (Fast2test 회원만 볼 수 있음)
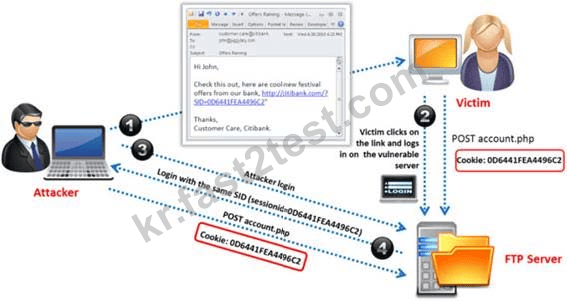
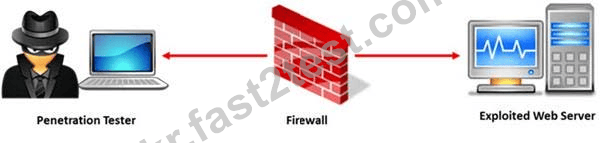
Identify the attack represented in the diagram below:
정답: A
설명: (Fast2test 회원만 볼 수 있음)
A penetration test will show you the vulnerabilities in the target system and the risks associated with it. An educated valuation of the risk will be performed so that the vulnerabilities can be reported as High/Medium/Low risk issues.
What are the two types of 'white-box' penetration testing?
What are the two types of 'white-box' penetration testing?
정답: D